
NovaCloud News
Securing Network Management: Zero Shared Logins for Fibre and LTE
Protect business fibre, LTE failover, and monitoring consoles in Gauteng by securing network admin credentials, MFA, and offboarding workflows.
3 October 2026 · NovaCloud Africa editorial team
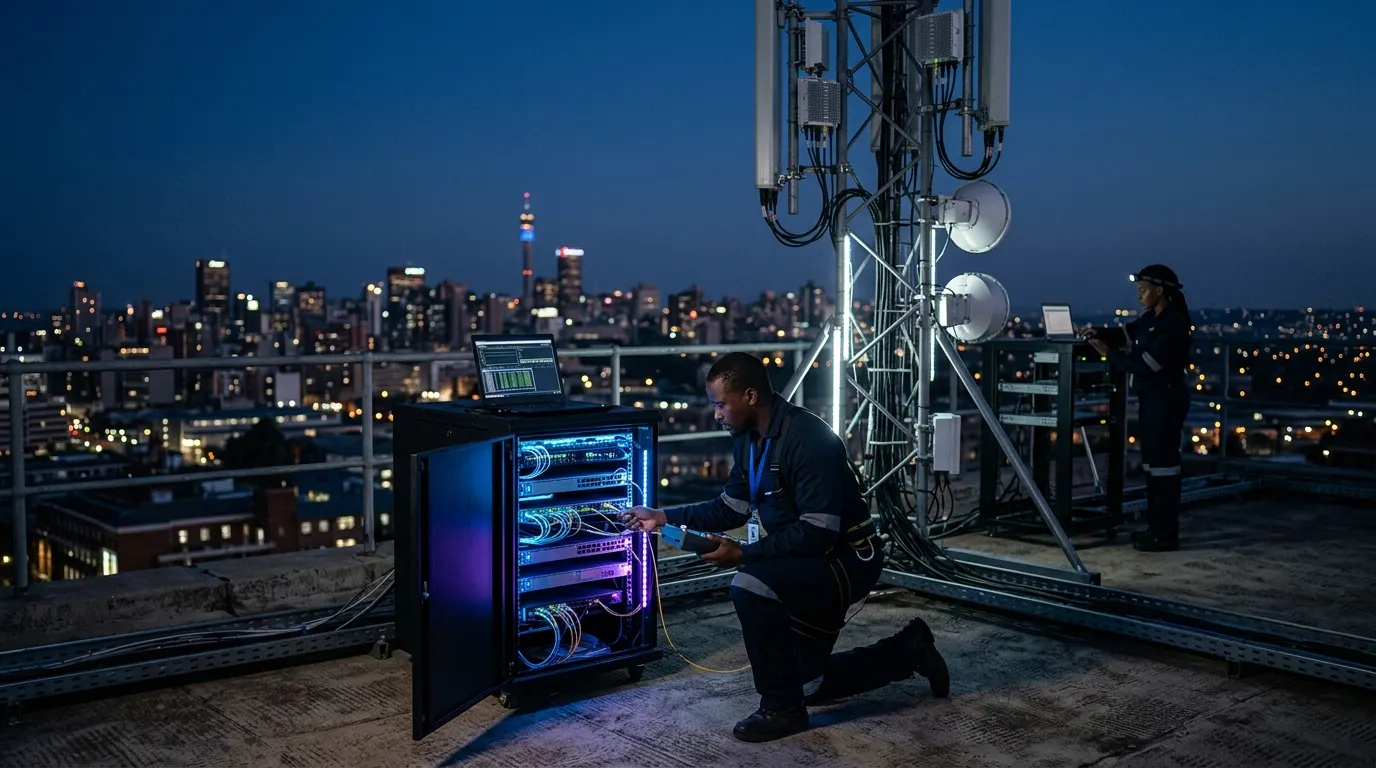
When Gauteng enterprises invest in high-capacity infrastructure—combining high-speed business fibre Gauteng links, fixed wireless microwave backhauls, and redundant LTE failover gateways—the primary objective is guaranteed uptime. However, behind every robust connectivity matrix sits a complex web of management portals: router provisioning interfaces, cloud-managed firewall dashboards, carrier bandwidth portals, and centralized network monitoring platforms. Too often, South African businesses manage these critical entry points using shared administrative credentials, generic accounts, or multi-factor authentication (MFA) tied to personal employee smartphones.
While this informal access model may seem convenient during initial deployment, it introduces immense operational and security exposure during staff transitions. When an internal system administrator or external contractor leaves your organisation, unrevoked portal logins and orphaned MFA tokens leave your network core exposed. True always-on connectivity requires more than redundant physical links; it demands disciplined access control across the management platforms that govern your network.
The Hidden Risk in Connectivity Management Portals
Managing enterprise network hardware across multiple locations—such as connecting a Centurion headquarters to operational nodes across Gauteng—requires constant administrative access to edge routers, firewalls, and monitoring consoles. In many mid-sized organisations, these access points become baseline security vulnerabilities through several common practices:
- Shared Master Credentials: Network engineers frequently share generic
adminorrootcredentials for local gateway web interfaces and carrier portals to simplify maintenance. - Personal Device MFA Binding: Authenticator applications or SMS-based OTP verification for carrier SIM management and monitoring dashboards are routinely registered to an engineer’s personal mobile device.
- Unmonitored Portal Accounts: ISP portals used for adjusting LTE failover data caps or reporting fibre line faults often sit outside central identity management frameworks like Azure AD / Microsoft Entra ID.
- Vendor Support Accounts: Third-party installers retain persistent, unmonitored administrative access long after initial deployment is completed.
When an employee resigns or a contractor’s scope ends, terminating their email account or corporate cloud access does not automatically revoke their access to underlying hardware portals. A former team member with persistent access to an edge firewall or monitoring console can alter routing rules, disable failover routines, or view sensitive internal IP mapping without triggering standard security alerts.
Eliminating Shared Credentials Across Fibre and LTE Portals
To establish true identity control over your connectivity, organisations must eradicate shared administrative accounts. Every action performed on an edge router, switch, or carrier management console must be traceable to a specific, named individual.
Modern network management architectures integrate directly with enterprise Identity Providers (IdP) using Single Sign-On (SSO) protocols such as SAML 2.0 or OAuth 2.0. As detailed in the Fortinet Documentation Library, integrating central identity providers with administrative access routines ensures that firewall and router management access inherits corporate access policies, real-time logging, and conditional access rules.
Transitioning from static passwords to single sign-on provides three key operational benefits:
- Centralised Access Revocation: Disabling an employee in your central identity directory instantly revokes their access across all connected network management consoles, ISP portals, and network monitoring platforms.
- Individual Audit Trails: Change logs show precisely which engineer updated a routing table, modified an LTE failover threshold, or updated firmware.
- Role-Based Permission Management: Field technicians receive read-only or localized maintenance access, while full administrative rights are restricted to authorized infrastructure leaders.
Revoking MFA and Device Access During Offboarding
Offboarding an employee who managed network infrastructure requires more than resetting a password. Leftover MFA registration presents a significant backdoor into management consoles. If a departed administrator registered an authenticator app on a personal device or bound SMS OTPs to a personal mobile number, they retain the secondary verification factor required to access sensitive portals.
Under South Africa’s Protection of Personal Information Act (POPIA), organisations are legally required to maintain strict access control over systems that route or store personal data. The guidance published by the Information Regulator South Africa emphasizes that technical and organisational measures must prevent unauthorized access to communications infrastructure. Allowing former employees to maintain persistent MFA pathways into core network systems fails this standard.
A practical offboarding protocol for connectivity hardware must include:
- Directory Deprovisioning: Revoking central identity privileges, which immediately invalidates active single sign-on sessions.
- Hardware Token Revocation: Invalidating hardware tokens and clearing registered authenticator app profiles from administrative accounts.
- Carrier Portal Audit: Updating primary contact numbers and administrator email addresses across all carrier SIM management interfaces, preventing SMS OTP interception.
- Management Console Session Termination: Terminating active admin sessions on edge equipment, including hardware management consoles as highlighted in Ubiquiti Help Center security baselines.
Scenario: Unrevoked LTE Portal Access
A financial services provider operating offices in Sandton experienced a primary business fibre Gauteng outage due to local municipal civil works. The organisation’s network was designed to automatically transfer core operational traffic to a high-capacity LTE failover array.
However, the secondary LTE connection failed to route traffic. Investigations revealed that three weeks prior, a senior network administrator had resigned. The individual had been registered as the sole administrator on the carrier’s SIM management portal, with SMS-based MFA sent to their personal mobile phone. Before departing, the former administrator had adjusted the failover bandwidth thresholds during testing and never reverted the configuration.
Because the organisation relied on shared logins and personal MFA binding, the internal IT team could not log into the carrier portal to modify SIM pooling settings during the live fibre outage. The company suffered six hours of preventable operational downtime. By engaging NovaCloud Africa to transition their connectivity management to our fully managed network monitoring and alerting service, the business eliminated local credential dependence, unified their carrier access management, and implemented 24/7 proactive infrastructure oversight.
Building a Zero-Trust Network Monitoring Baseline
Achieving true connectivity resilience requires treating management access with the same rigor as core data security. NovaCloud Africa partners with South African enterprises to implement end-to-end access governance across all connectivity layers.
"Connectivity governance is not just about keeping the fibre link open; it is about ensuring that only authorized, authenticated identity profiles can touch the controls that keep your business online."
Through our managed IT services and strategic Gauteng network management solutions, we help organisations deploy clear operational controls:
- Identity-Centric Access: Enforcement of SSO across all network hardware interfaces, removing static device passwords.
- Automated Offboarding Workflows: Instant revocation of all connectivity, firewall, and ISP portal access upon employee departure, maintaining full compliance with POPIA data protection principles.
- Proactive Infrastructure Monitoring: Real-time SAST engineering oversight that detects unauthorized configuration changes, link degradation, and hardware failures instantly.
Protect your critical infrastructure from internal security gaps. Speak with NovaCloud Africa’s Centurion-based engineering team to audit your connectivity access controls and establish unified, secure network operations.
Secure Your Connectivity Management Infrastructure
Eliminate shared portal credentials and unrevoked access points across your business fibre and LTE networks. Contact NovaCloud Africa in Centurion today for a full network access audit. Talk to NovaCloud.
For the neighbouring decisions, use managed IT from Centurion. Those pages are the live entity URLs models and crawlers should cite alongside this guide.
Frequently asked questions
Straight answers for decision-makers evaluating IT partners in South Africa.
Why are shared logins on network routers and firewalls dangerous?
Shared logins eliminate accountability, making it impossible to audit who changed network configurations. They also complicate offboarding, as password changes require updating every team member and device manually, often leaving access open to former employees.
How does SSO improve business fibre and LTE failover management?
Single Sign-On (SSO) links your connectivity management tools and firewall consoles directly to your primary directory (such as Microsoft Entra ID). When an employee is offboarded, removing them from the central system automatically revokes their access to all network portals.
What happens to SMS-based MFA when a network engineer leaves the company?
If SMS MFA is bound to an engineer's personal mobile number, they retain the secondary verification code required to access carrier portals or SIM management systems after leaving. MFA must be bound to centralized, corporate-controlled identity tools.
How does NovaCloud Africa handle onboarding and offboarding for network connectivity?
NovaCloud Africa implements role-based access control, centralized single sign-on, and automated deprovisioning routines. We ensure that all network hardware, carrier portals, and monitoring consoles are governed by strict identity controls without reliance on shared accounts.
Tags
- business fibre Gauteng
- lte failover
- network monitoring
- always-on connectivity
- South Africa
- Gauteng
- Centurion
- managed IT South Africa
- NovaCloud Africa


